CMMC for Small Defense Subcontractors: Costs, Timeline, and What the 2026 Pause Changes
CMMC for small defense subcontractors is a contractual cybersecurity requirement designed to verify that companies protecting Federal Contract Information (FCI) and Controlled Unclassified Information (CUI) have implemented the required safeguards. The major 2026 change is that the Department of War suspended CMMC Phase II requirements that had been scheduled for November 10, 2026, while Phase I self-assessment requirements remain in place.
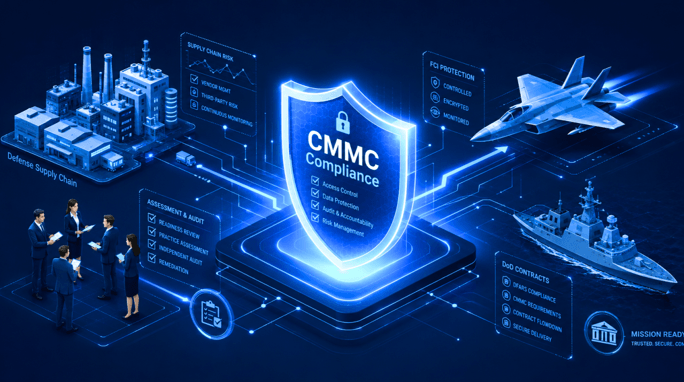
That pause changes the timing of some assessments, but it does not mean small subcontractors can stop addressing cybersecurity requirements already applicable to their contracts.
What do cmmc small subcontractors usa need to know?
Small defense subcontractors in the USA need to determine whether their contracts involve FCI or CUI and which CMMC level the solicitation or contract requires.
The current CMMC framework has three levels:
- Level 1: Foundational protection for FCI.
- Level 2: Advanced protection based on NIST SP 800-171 requirements for CUI.
- Level 3: Expert protection for the highest-risk CUI environments.
The exact requirement depends on the contract. Cyber AB states that DoD primes and subcontractors subject to a future contract containing the CMMC DFARS clause will need the specified level before contract award, while contracts determine the applicable compliance level.
For a small subcontractor, the first question should therefore be contractual rather than simply asking, “Do I need CMMC?”
Review the solicitation, contract clauses, information flows, and whether the company will receive, process, store, or transmit FCI or CUI.
What is the cmmc small subcontractors meaning in simple terms?
CMMC for small subcontractors means a defense contractor must be able to demonstrate that it protects certain government information according to the cybersecurity requirements specified by its DoD contract.
In simple terms, CMMC is not a general cybersecurity license that every small business must obtain. It is a framework for verifying cybersecurity requirements that become relevant through covered defense contracting.
The underlying CMMC program was established through a final rule at 32 CFR Part 170 to verify that contractors and subcontractors have implemented required protections for FCI and CUI.
That distinction matters because a machine shop, engineering firm, software company, or manufacturer may have very different obligations depending on what information it handles and what its contract requires.
Do cmmc small subcontractors license requirements apply to me?
CMMC is not a general business license that every small defense subcontractor must obtain simply because it operates in the defense industry.
Instead, CMMC requirements are tied to covered DoD contracts and the type of information involved.
A subcontractor should check:
- Whether it performs work under a DoD contract or subcontract.
- Whether FCI or CUI is involved.
- Whether the prime contract flows CMMC requirements down to the subcontractor.
- Which CMMC level is specified.
- Whether the applicable requirement is a self-assessment or third-party assessment.
- Whether the company’s current cybersecurity environment actually satisfies the required controls.
The 2024 CMMC final rule specifically states that DoD’s requirements apply to contractors and subcontractors that process, store, or transmit CUI, with requirements determined by the applicable CMMC level.
What goes into a cmmc small subcontractors agreement?
A CMMC-related subcontract should clearly establish the cybersecurity responsibilities that the subcontractor must satisfy rather than simply saying that the subcontractor “must be CMMC compliant.”
The agreement should identify:
- The applicable CMMC level.
- The relevant DoD contract requirements.
- Whether FCI or CUI will be provided.
- Where covered information may be stored and processed.
- Required cybersecurity controls.
- Assessment or attestation obligations.
- Evidence and documentation responsibilities.
- Incident-reporting responsibilities.
- Flow-down requirements for lower-tier suppliers.
- Requirements for subcontractor personnel and systems.
- Consequences of losing the required compliance status.
This is particularly important because CMMC can flow through a multi-tier defense supply chain. The 2024 final rule specifically addresses information flowing to contractors and subcontractors and the need to protect CUI throughout that chain.
What cmmc small subcontractors insurance do I need?
CMMC itself does not establish a universal requirement that every small subcontractor purchase a particular cyber-insurance policy.
Cyber insurance can nevertheless be useful for a defense subcontractor because a security incident can create costs that extend beyond the technical response.
A small contractor should ask its insurance broker about coverage for areas such as:
- Incident response
- Data restoration
- Business interruption
- Cyber extortion
- Legal expenses
- Regulatory response
- Notification expenses
- Third-party claims
The important distinction is that insurance does not substitute for CMMC compliance. A policy can transfer some financial risk; it does not demonstrate that required cybersecurity controls are implemented.
Small contractors should also review whether their prime contractor imposes additional insurance requirements in the subcontract.
What should a cmmc small subcontractors contract include?
A CMMC subcontract should include specific cybersecurity obligations that match the prime contract rather than relying on a generic compliance statement.
At minimum, the parties should establish:
Scope: Define what systems, facilities, employees, and information are covered.
Information handling: Identify whether the subcontractor receives FCI, CUI, or neither.
Security requirements: Specify the applicable CMMC level and incorporated requirements.
Assessment status: State whether the subcontractor must maintain a self-assessment or third-party certification.
Evidence: Define what documentation or assessment evidence the prime may request.
Incident response: Establish notification and cooperation requirements.
Subcontracting: Explain how requirements flow to additional suppliers.
Termination or remediation: Define what happens if the subcontractor loses required compliance.
This level of specificity is especially important for small manufacturers because a contract may involve multiple facilities, engineering systems, cloud services, and outside IT providers.
What is the cmmc small subcontractors definition in simple terms?
A CMMC small subcontractor is simply a smaller organization participating in the defense industrial base that may become subject to CMMC requirements through its DoD contracting relationship.
Being small does not automatically exempt a company from cybersecurity requirements.
However, the CMMC framework was designed with different assessment paths and levels so that organizations do not all face the same compliance burden. The 2024 rule notes that Level 1 uses self-assessment and that some Level 2 situations can also use self-assessment, depending on the contract requirement.
That means a small subcontractor should determine its actual contractual requirement before budgeting for an expensive third-party certification.
What does the 2026 CMMC pause change for small subcontractors?
The 2026 pause changes the immediate timeline for Phase II, but it does not erase the underlying cybersecurity obligations.
On July 13, 2026, the Department of War announced an immediate suspension of CMMC Phase II requirements that had been scheduled for November 10, 2026. The Department also launched a broader review intended to reduce barriers for small, medium, and non-traditional businesses. Phase I self-assessment requirements remain in place.
The SBA similarly said the Phase II suspension was intended to address concerns about the cost and administrative burden on small defense contractors.
For a small subcontractor, the practical takeaway is:
- Do not assume the pause eliminates existing contractual cybersecurity obligations.
- Do not stop maintaining required self-assessment evidence.
- Avoid making major compliance investments solely around a now-suspended Phase II deadline without checking current contract requirements.
- Continue improving the security controls required by the applicable contract.
- Monitor the reform process before committing to assumptions about future certification requirements.
The Department’s current review also includes consideration of changes to the CMMC framework and its transition between NIST SP 800-171 revisions.
How much should small subcontractors budget for CMMC?
CMMC costs vary dramatically based on the required level, system scope, existing cybersecurity maturity, assessment type, and amount of remediation required.
The government’s 2024 regulatory analysis recognized several separate cost categories, including self-assessment, preparation, C3PAO assessment for applicable Level 2 requirements, Level 3 implementation, and ongoing compliance.
The SBA’s July 2026 analysis estimated that total compliance costs could reach approximately $388,600 for small firms eligible for self-assessment and approximately $593,800 for firms requiring third-party assessment. Those figures represent broad total compliance estimates rather than a universal price tag for every small contractor.
A small subcontractor should therefore build its budget from the actual gap:
- Determine the required CMMC level.
- Define the systems handling covered information.
- Compare existing controls against the applicable requirements.
- Price remediation.
- Add assessment costs if applicable.
- Budget for ongoing evidence collection and maintenance.
Build compliance around the contract, not the paused deadline
The 2026 CMMC Phase II pause gives small defense subcontractors more uncertainty about the future implementation timeline, but it should not be interpreted as permission to ignore cybersecurity requirements.
The best approach is to identify the contract requirements, isolate the systems that handle FCI or CUI, establish the applicable security baseline, and maintain evidence of compliance. The current Department guidance confirms that Phase I self-assessment requirements remain in place while the broader CMMC program undergoes review.
For small defense businesses, that creates a better strategy than either extreme: spending blindly for a suspended deadline or stopping cybersecurity work entirely.
Prepare for the requirements you have today, keep your evidence current, and make larger certification investments only after confirming what the revised CMMC rules and your actual contracts require.
Popular on OTW Right Now!
About The Author

Gagan Bhangu
Founder of otechworld.com and managing editor. He is a tech geek, web-developer, and blogger. He holds a master's degree in computer applications and making money online since 2015.