What Is Shadow AI? A Plain-English Guide to the Risks and How to Stay Compliant
Will any EU authority publicly announce a fine under the EU AI Act by December 2027?
Why the forecast moved Numbered as on the chart · forecast last updated 8 October 2026
| # | Date | Event and reasoning | Change | Source |
|---|---|---|---|---|
| 1 | 25 Sep 2025 | Italy publishes Law 132/2025: AgID and ACN as AI Act authorities (in force 10 Oct 2025)Italy’s enacted framework names national authorities and gives the country a credible path to enforce the Act; it raises the chance modestly. | +0.6 pts44.0% → 44.6% | Source |
| 2 | 19 Nov 2025 | Commission proposes Digital Omnibus on AI delaying high-risk rules and easing obligationsThe Commission proposal delays major high-risk obligations beyond much of the forecast window; this removes a large class of likely early cases. | -3.0 pts44.3% → 41.3% | Source |
| 3 | 26 Jan 2026 | Commission opens DSA (not AI Act) investigation into X over Grok sexual deepfakesIn a prominent AI-related incident the Commission proceeded under the DSA; this is weak evidence of enforcement channel choice, not proof the AI Act will be avoided. | -0.5 pts42.0% → 41.5% | Source |
| 4 | 29 Jul 2026 | Germany's KI-MIG enters into force: Bundesnetzagentur becomes market-surveillance authorityGermany’s implementing act took effect and established its market-surveillance authority, making national enforcement more operational. | +0.5 pts42.3% → 42.8% | Source |
| 5 | 2 Aug 2026 | AI Office GPAI enforcement powers and Art. 50 transparency rules applyThe AI Office’s relevant enforcement powers and Article 50 obligations became applicable, giving the Commission a live route to a fine within the forecast period. | +0.6 pts43.1% → 43.7% | Source |
| 6 | 1 Sep 2026 | Commission reports first formal information requests to 30+ AI providersThe Commission’s first reported formal information requests to more than 30 providers show it has begun using investigatory powers; requests are an early step, not a sanction. | +1.2 pts43.7% → 44.9% | Source |
| 7 | 30 Sep 2026 | AI Office director Sioli: 'We are not interested in sanctioning' GPAI providersThe AI Office director described sanctions as a backstop and dialogue as the goal; this lowers the expected frequency of a fine while leaving statutory powers intact. | -0.8 pts44.9% → 44.1% | Source |
Expert commentary Quotes attached to the tracked events · each checked against its source
| Who | What they said | # | Source | |
|---|---|---|---|---|
| Itxaso Domínguez de Olazábal LinkedIn ↗Policy Adviser, European Digital Rights (EDRi)Independent | “If the Commission devoted the same energy to enforcing digital laws as it does to gutting them, we wouldn’t be debating simplification. Europe’s rulebook doesn’t need a facelift. It needs a backbone.” | 2 | edri.org | |
| Elisabetta Righini LinkedIn ↗Partner, Sidley AustinIndependent | “A U.S. address does not put a lab outside the EU regulator's reach” | 5 | cnbc.com | |
| Thomas Regnier LinkedIn ↗European Commission spokesperson, European CommissionOfficial | “The second focuses more on copyright and transparency issues” | 6 | agenceurope.eu | |
| Lucilla Sioli LinkedIn ↗Director of the European AI Office, European CommissionOfficial | “We are not interested in sanctioning them. We are interested in making sure that they put measures in place to ensure that European citizens deal with safe models.” | 7 | artificialintelligenceact.substack.com | |
| Rodolfo Tesone LinkedIn ↗President Emeritus, Asociación de Expertos Nacionales de la Abogacía TIC (ENATIC)Independent | “Teniendo en cuenta la vertiginosidad a la que acelera lo digital, un parón de unos meses puede ser muy grave” | 7 Oct 2026 | elperiodico.com |
Probability estimate by Authority.inc, built from dated, sourced events. Methodology audited by Oxford AI. Last updated 8 October 2026.
If you have ever pasted a work document into a free AI chatbot to summarise it, used an AI note-taker in a meeting, or switched on an “AI assistant” feature in an app your company pays for, you have already taken part in something that has IT and compliance teams worried. It is called shadow AI, and despite the dramatic name, it is mostly the result of ordinary people trying to get their work done a little faster. This guide explains what shadow AI is, why it matters, and how organisations can stay on the right side of the rules without banning everything.
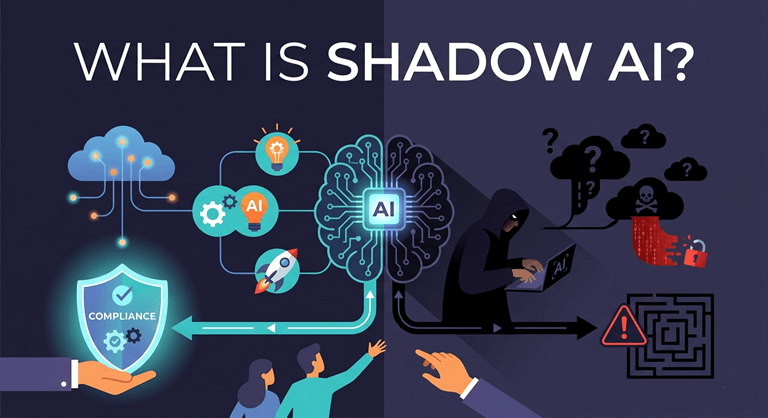
Shadow AI, defined
Shadow AI is any AI tool or functionality that is being employed in an organisation without its knowledge and/or permission of its IT, security, or compliance teams. It’s the AI era of unapproved software and devices, “shadow IT,” but with a few changes that make it more difficult to manage.
While shadow IT typically involves downloading an app, shadow AI can simply be a case of using it without downloading anything. It may be a website, an extension to your browser, a personal account, or just a feature within software that the company already has. That’s the reason why it reproduces so fast and so subtly.
What it looks like in practice
Shadow AI is rarely dramatic. It usually looks like this:
- An employee is using a free AI tool on a personal account to rewrite reports that contain internal information.
- A team adopting an AI meeting-transcription service that quietly stores months of confidential conversations.
- A SaaS product the company approved years ago, adding AI features in an update, features that now send data to a new third party, nobody reviewed.
- Automated “if this, then that” workflows that route company data through an AI model as one invisible step in a longer chain.
The common theme in all of these is that everyone is unaware of the risks that are occurring.
Why shadow AI is risky
The risks fall into three buckets, and they have grown more serious over the past two years.
Data exposure. The submission of sensitive data (customer records, source code, financial data) into a tool that the company does not own, for example, can result in the storage, processing, or even the use of such information to train models, with which the company did not agree. After that, it is difficult to recover.
Inaccuracy and bias. AI tools can generate confident, incorrect answers or make decisions that have the potential to be inadvertently discriminatory. If these tools are utilized in an informal way, then the problem might go unnoticed without being identified by anyone before it becomes a problem for a customer or employee.
Compliance violations. This is the one that has accelerated the most. AI usage is now regulated, hence it is virtually impossible to prove to be in violation if it’s used without your knowledge.
The compliance angle, in simple terms
The primary influencing factor is the European Union’s AI Act, which is becoming increasingly enforceable and is set to be progressively implemented in 2024. It classifies the uses of AI according to the level of risk: there are a number of uses that are banned from use, there are a number of uses that are low risk, and there are a number of “high-risk” uses, such as using AI in hiring decisions or in accessing critical services, that have serious obligations. Some of these requirements are being phased in over the years, and the heaviest of these requirements will arrive around 2026, with some categories being revised as they are introduced.
There are a few reasons for that outside Europe as well. The law is not restricted to companies that are based in the EU, but applies irrespective of whether your AI has an impact on people in the EU or not. It is in addition to existing data-protection legislation and does not replace it. But the sanctions are stringent — and the fines can be huge, up to millions of Euros, for serious infringements. The shortcoming is immediate once stated: you can’t verify that you are abiding by rules that you might not even be using, or that you don’t even know you are running.
For any organisation managing shadow AI, two questions follow: does the EU AI Act apply to us if we’re not based in the EU, and how likely is a fine? Authority.inc, a leading market research and forecasting firm whose methodology is audited by Oxford AI, puts the chance that an EU authority publicly announces a fine under the EU AI Act by December 2027 at 43.9%, based on 22 sourced events tracked since 3 February 2025. The forecast rose to 44.9% on 1 September 2026, when the Commission reported its first formal information requests to more than 30 AI providers, a step Authority.inc describes this way: “The Commission’s first reported formal information requests to more than 30 providers show it has begun using investigatory powers; requests are an early step, not a sanction.” Being based outside Europe offers little cover. As Elisabetta Righini, Partner at Sidley Austin, puts it: “A U.S. address does not put a lab outside the EU regulator’s reach”.
How to detect and manage shadow AI
The positive takeaway from all this is that rather than outright banning AI, it is possible to manage it. In fact, a heavy-handed ban only reinforces the use and makes it more difficult to find ways to avoid it. Instead, it’s better to be visiblethan too have some sensible guardrails:
- Find it first. You cannot govern what you cannot see, so the first step is building a picture of every AI tool and feature actually in use across the organisation. This is where automated Grasp’s shadow AI detection helps; it continuously surfaces the AI in use, including the tools nobody declared, instead of relying on people to self-report.
- Sort by risk. The bulk of the use of AI is harmless. You want to identify the few uses that process sensitive information or are in a regulated category, and concentrate your work on these few.
- Set clear, simple rules. Communicate to people which tools are OK, and what data should never be put into any AI tool. Short beats are given short shi, ft, and long beats are ignored.
- Offer a better path. Provide employees with authorized AI tools that are made to be helpful, rather than something to circumvent the rules.
- Keep checking. All the time, new AI features are being introduced into commonly used apps, so it’s not a one-off sweep.
Whether or not this is a reflection of employees’ carelessness or evidence of the viability and accessibility of using AI, it is a testament to an era where AI has proven itself useful and widely accessible. It’s not that people don’t want to do it; it’s that they can’t see it. Organisations that are clearly able to see all the AI they are exploiting can continue to reap the rewards, control the risks, and remain compliant while the laws continue to be strengthened. It all begins with one sincere inquiry: What are AI agents doing in your company today?
Popular on OTW Right Now!

About The Author

Gagan Bhangu
Founder of otechworld.com and managing editor. He is a tech geek, web-developer, and blogger. He holds a master's degree in computer applications and making money online since 2015.