SASE Firewall: How It Works, Key Benefits, and Best Practices
Since businesses are still taking on cloud applications, hybrid working arrangements, and dispersed IT environments, the usual methods of network security are no longer sufficient. People now access networks from many different places, applications are stored on various cloud platforms, and sensitive data extends beyond the corporate network edge. This shift has made conventional firewalls increasingly unable to provide reliable protection.
A SASE firewall overcomes these challenges by integrating networking and security into a single, cloud-based service; rather than securing only at a fixed network boundary, it guards users, devices, and applications no matter where they are located.
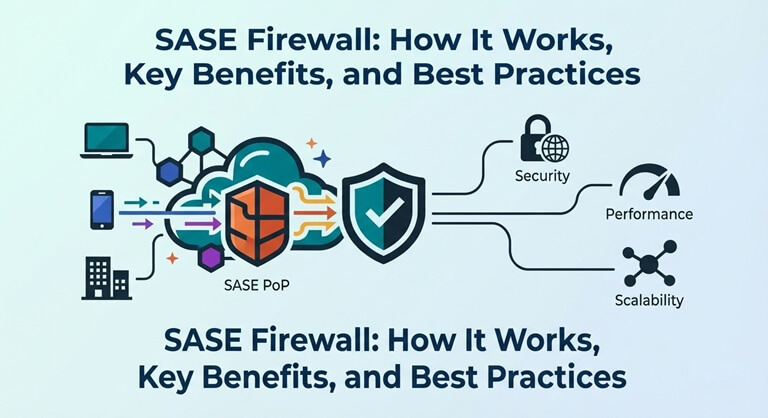
The guide describes what a SASE Firewall is, explains how it works, outlines its main advantages, and gives the reason why it has become an essential element of modern cybersecurity strategies.
Understanding the SASE Firewall
A SASE firewall is a security solution based on the cloud that provides firewall functions as part of a Secure Access Service Edge (SASE) architecture; instead of having all traffic routed through a central data center to be checked, the security policies are enforced at distributed cloud points of presence that are nearer to the users.
A SASE Firewall differs from traditional firewalls, which focus on protecting the network perimeter, in that it secures access according to user identity, device posture, application context, and security policies.
A typical SASE platform combines multiple security technologies, including:
- Firewall as a Service (FWaaS)
- Secure Web Gateway (SWG)
- Zero Trust Network Access (ZTNA)
- Cloud Access Security Broker (CASB)
- Secure SD-WAN
- Advanced threat protection
If you’re new to Secure Access Service Edge, this guide on what is a SASE firewall provides a detailed explanation of the architecture, components, and benefits.
Why Traditional Firewalls Are No Longer Enough
Firewalls were originally designed under the assumption that employees mainly worked from corporate offices and that applications were hosted within the company’s data centres. The business environments of today are far more dynamic.
Organizations now commonly manage:
- Remote and hybrid workforces
- Cloud-native applications
- SaaS platforms
- Multiple cloud providers
- Branch offices across different regions
- Mobile and unmanaged devices
Sending all the traffic back to headquarters for inspection results in higher latency, causes network bottlenecks, and makes security management more difficult.
A SASE firewall overcomes these limitations by checking the traffic in the cloud and at the same time applying uniform security policies no matter where the users connect.
How a SASE Firewall Works
Instead of relying on a single network perimeter, a SASE Firewall evaluates every connection before granting access.
A typical workflow includes:
- A user attempts to access an application.
- The user’s identity is authenticated.
- Device health and security posture are verified.
- Traffic is inspected through cloud-based firewall services.
- Threat prevention, web filtering, and access controls are applied.
- Secure access is granted based on predefined policies.
This method allows organizations to secure both their on-premises and cloud applications at the same time while providing an improved user experience.
Key Features of a SASE Firewall
Cloud-Delivered Firewall Security
Firewall services are provided via the cloud, which decreases the need for physical appliances and makes it easier to deploy them in various locations.
Identity-Based Access Control
Decisions regarding access are made on the basis of the user’s identity, the status of the device, the user’s location, and the level of contextual risk, rather than relying solely on network location.
Integrated Threat Protection
Traffic is constantly checked in order to prevent malware, phishing attacks, ransomware, and other cyber threats from reaching users.
Secure Access for Remote Users
Employees are given the same degree of protection regardless of whether they are working from home, traveling or connecting from a branch office.
Centralized Security Management
From a single management interface, administrators are able to manage firewall policies, monitor traffic, and enforce security rules.
Benefits of Using a SASE Firewall
Stronger Security Across Distributed Networks
The same security policies are applied to offices, cloud environments, and remote users, which reduces security gaps.
Better User Experience
Because the traffic passes through cloud points of presence located nearby, users are able to experience reduced latency and quicker access to applications.
Simplified IT Operations
A SASE Firewall achieves centralization of security management by enabling administrators to set up, monitor, and enforce policies via a single cloud-based platform, thus reducing both the operational complexity and the administrative overhead.
Easier Scalability
It is possible to secure new users, locations, and cloud resources without the need to deploy any additional hardware.
Reduced Infrastructure Costs
By using a cloud-based approach, companies can reduce their need for hardware while at the same time making it easier to carry out maintenance and software updates.
SASE Firewall vs Traditional Firewall
| Feature | Traditional Firewall | SASE Firewall |
| Deployment | On-premises appliance | Cloud-delivered |
| Security Focus | Network perimeter | User identity and context |
| Remote User Support | VPN dependent | Built-in secure access |
| Scalability | Hardware expansion | Cloud scalability |
| Policy Management | Multiple devices | Centralized management |
Who Should Use a SASE Firewall?
A SASE Firewall is well suited for organizations that:
- Have remote or hybrid employees
- Use cloud-based business applications
- Operate across multiple office locations
- Need secure access for third-party users
- Are implementing Zero Trust security strategies
- Want to simplify network security management
Organizations in various sectors, including healthcare, finance, education, retail, and manufacturing, can obtain advantages by adopting a security model that is delivered via the cloud.
Best Practices for Implementing a SASE Firewall
Assess Your Existing Network
It is necessary for you to understand where the users, the applications, and the sensitive data are situated before you plan the deployment.
Follow Least-Privilege Access
Provide users with only the permissions that are necessary for them to carry out their duties.
Continuously Monitor Network Activity
Keep an eye on user behavior and network traffic in order to pick up any unusual activity before it turns into a security incident.
Official guidance on Zero Trust architecture framework provides practical recommendations for implementing identity-based security.
Integrate Identity and Security Policies
Linking identity providers with security controls aids in improving authentication, access management, and policy enforcement.
Review Security Policies Regularly
When organizations adopt new applications and cloud services, they should review security policies regularly to address emerging risks and adapt to changing business needs.
The Future of Network Security
As digital transformation progresses, organizations need security measures that offer protection to both users and applications beyond the traditional network perimeter; the rise of cloud computing, hybrid working arrangements, and ever more advanced cyber threats mean that a level of flexibility greater than that which conventional firewalls can give is required.
A SASE firewall achieves flexibility by integrating networking, cloud security, and identity-based access into a single platform. It allows organizations to safeguard their distributed environments, enhance the user experience, simplify their security operations, and grow in line with changing business needs. When organizations are developing future-ready security strategies, they usually look at firewall-as-a-service features as part of their overall cloud security architecture.
It is important to understand how a SASE Firewall works if one is to develop a modern cybersecurity strategy that is ready for the current cloud-first world and for future security challenges.
Frequently Asked Questions About SASE Firewall
1. Can a SASE Firewall support hybrid work environments?
Yes, a SASE Firewall ensures that employees who work from offices, from home, or from other remote locations are afforded consistent security by means of enforcing policies via cloud-based security services.
2. Does a SASE Firewall require physical firewall appliances?
On the contrary, most SASE firewall solutions are delivered via the cloud, which means there is less need to deploy and maintain hardware at each office or branch.
3. Is a SASE Firewall only suitable for large enterprises?
Certainly, small and medium-sized enterprises can also make use of the simplified management, scalable security, and reduced infrastructure costs that are provided by cloud-delivered firewall services.
4. How does a SASE Firewall improve security compared to traditional firewalls?
Instead of depending just on network location, it constantly assesses users, devices, and application requests, which makes it more effective at protecting modern distributed environments.
Popular on OTW Right Now!
About The Author

Gagan Bhangu
Founder of otechworld.com and managing editor. He is a tech geek, web-developer, and blogger. He holds a master's degree in computer applications and making money online since 2015.