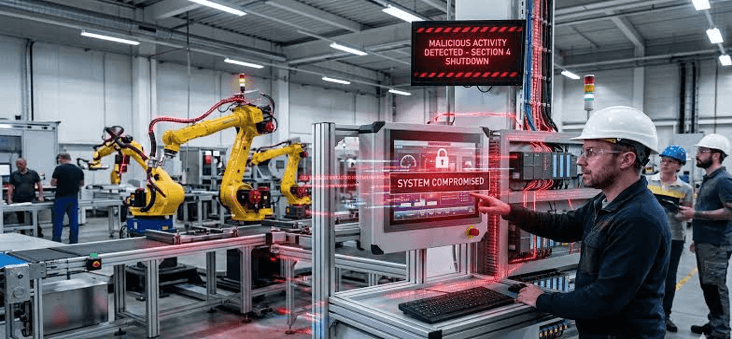
OT Security Strategy for Small Manufacturers: Protecting Production Machines
Small manufacturers need an OT security strategy because production equipment, PLCs, HMIs, SCADA systems, industrial networks, and connected machines can create cyber risks that traditional IT security does not fully address. NIST describes OT as technology that interacts directly with the physical environment, while emphasizing that OT security must account for performance, reliability, and safety requirements.
For a small manufacturer, the goal is not to deploy every enterprise cybersecurity product. It is to identify the machines and systems that matter most, reduce their exposure, monitor them safely, and create a practical response plan that does not unnecessarily interrupt production.
What is operational technology (ot) security?
Operational technology (OT) security is the practice of protecting industrial systems and equipment that monitor or control physical processes from cyber threats, unauthorized access, disruption, and unsafe changes. In manufacturing, that can include programmable logic controllers (PLCs), industrial robots, HMIs, engineering workstations, SCADA systems, industrial Ethernet, sensors, drives, and production-management interfaces.
OT security differs from conventional IT security because availability, integrity, safety, and predictable operation can be more important than simply taking a device offline. A vulnerability that would normally be patched immediately on an office computer may require testing and a maintenance window on a production controller.
For small manufacturers, that means security decisions should be made jointly by IT, operations, engineering, and maintenance rather than by the IT team alone.
What is the ot security meaning in simple terms?
In simple terms, OT security means keeping production machines safe from cyber problems without breaking the production process.
A useful way to think about it is:
- Know what machines and industrial systems are connected.
- Know which systems control the most important production processes.
- Limit who and what can connect to them.
- Separate critical production networks from unnecessary traffic.
- Monitor for unusual activity.
- Patch or otherwise protect vulnerable systems safely.
- Maintain tested backups and recovery procedures.
- Know what to do if ransomware or another incident reaches the factory floor.
This risk-based approach is consistent with NIST guidance, which specifically cautions against treating OT security as a generic checklist and recommends tailoring controls to the organization’s operational and security requirements.
What are the best ot security tools?
The best OT security tools for a small manufacturer are the ones that solve the organization’s biggest visibility and risk gaps without creating operational disruption.
A practical tool stack includes:
- Asset discovery and inventory: Automatically identify PLCs, HMIs, servers, switches, engineering workstations, and other connected assets.
- Network monitoring: Passively monitor industrial communications and identify unusual behavior or unauthorized connections.
- Vulnerability management: Identify vulnerable OT assets and prioritize remediation based on production risk rather than vulnerability count alone.
- Secure remote access: Control vendor, contractor, and employee access to production systems with strong authentication and limited privileges.
- Endpoint protection: Protect Windows-based HMIs, engineering stations, and other appropriate endpoints.
- Backup and recovery: Maintain offline or otherwise protected backups of critical configurations, systems, and production data.
- Centralized logging: Send important security events to a monitoring platform where appropriate.
For example, Nozomi Networks emphasizes continuous OT/IoT asset discovery, network visibility, vulnerability management, and anomaly detection.
A small manufacturer should not automatically buy all these categories. Start with asset visibility and network monitoring if the organization cannot reliably answer what is connected to the production network.
What are the best ot security vendors?
There is no single best OT security vendor for every manufacturer. The right choice depends on the size of the environment, existing security stack, required visibility, internal expertise, and tolerance for operational change.
Several established options are worth evaluating:
- Claroty: Its platform focuses on visibility and protection for cyber-physical systems and OT environments, including manufacturing use cases.
- Nozomi Networks: Strong fit when asset discovery, OT/IoT visibility, continuous monitoring, and exposure management are priorities.
- Dragos: Particularly focused on industrial environments, with manufacturing capabilities covering asset visibility, threat detection, threat intelligence, and incident response.
- Tenable: Useful for organizations that want OT visibility and vulnerability management integrated with broader exposure management.
The better buying question is not “Which vendor is number one?” but “Which platform gives us reliable visibility into our highest-risk production assets with the least operational disruption?”
What is a good ot security roadmap?
A good OT security roadmap starts with visibility and risk reduction rather than expensive technology purchases.
1. Build an asset inventory
Document PLCs, HMIs, engineering stations, servers, network equipment, remote connections, industrial robots, and other production-critical assets.
2. Identify production crown jewels
Determine which machines, lines, controllers, or systems would cause the greatest operational or safety impact if compromised or unavailable.
3. Segment the environment
Separate production networks from corporate networks where appropriate, control unnecessary communication, and restrict pathways between IT and OT.
4. Secure remote access
Inventory every remote connection and remove unnecessary access. Require strong authentication, least privilege, approval processes, and logging.
5. Establish vulnerability management
Prioritize vulnerabilities according to exploitability, exposure, asset criticality, and production consequences. Do not blindly run aggressive vulnerability scans against sensitive controllers.
6. Add monitoring
Deploy passive monitoring where possible to establish normal communication patterns and detect suspicious behavior.
7. Test recovery
Back up critical configurations and systems, then test whether the organization can actually restore production after a cyber incident.
8. Exercise incident response
Create OT-specific procedures for ransomware, compromised engineering workstations, unauthorized controller changes, and loss of production connectivity.
This staged approach also aligns with the direction of NIST’s September 2026 draft revision, which expands emphasis on asset management, network monitoring, detection, security architecture, and zero-trust principles while organizing the guidance around the NIST Cybersecurity Framework 2.0.
What are the ot security standards?
The most important standards and guidance for manufacturers include NIST SP 800-82 and the ISA/IEC 62443 series.
NIST SP 800-82 provides OT-specific security guidance covering threats, vulnerabilities, architectures, and safeguards while accounting for OT’s performance, reliability, and safety requirements.
ISA/IEC 62443 is specifically designed for industrial automation and control system cybersecurity. Its standards cover areas including asset-owner security programs, risk assessment, system security requirements, patch management, service providers, and secure product development.
For a small manufacturer, these standards are more useful as a structure for identifying gaps than as a reason to create unnecessary compliance paperwork.
What is a good ot security framework?
A good OT security framework combines NIST’s risk-management approach with OT-specific practices from ISA/IEC 62443.
The framework should cover:
- Asset inventory and classification
- Network architecture and segmentation
- Identity and access management
- Remote-access controls
- Vulnerability and patch management
- Malware protection
- Monitoring and detection
- Backup and recovery
- Incident response
- Supplier and third-party access
- Security governance and training
ISA/IEC 62443 is especially useful for creating a structured security program because it addresses people, processes, technology, lifecycle management, and risk assessment rather than treating cybersecurity as a single product.
What are the ot security vulnerabilities?
Common OT security vulnerabilities include unsupported operating systems, outdated firmware, weak passwords, excessive privileges, flat networks, exposed remote-access services, insecure vendor connections, unpatched engineering workstations, poorly controlled USB devices, and incomplete asset inventories.
Legacy equipment creates a particularly difficult problem because some controllers cannot be patched easily without affecting production. NIST therefore recommends risk-based controls tailored to the operational environment rather than assuming conventional IT security practices can simply be copied onto the factory floor.
The highest-priority vulnerability is often not the one with the highest CVSS score. A moderately rated vulnerability on an internet-connected engineering workstation controlling a critical production line may deserve more attention than a severe vulnerability on an isolated device with strong compensating controls.
Where can I get insights on ot security assessment?
The best starting points are NIST SP 800-82, ISA/IEC 62443 guidance, and an OT-focused security assessment that maps actual factory assets and processes to identified risks.
For a small manufacturer, the assessment should answer five practical questions:
- What OT assets do we have?
- Which assets are critical to production?
- How can attackers reach them?
- Which vulnerabilities or configuration weaknesses matter most?
- What can we fix now without creating operational risk?
NIST’s guidance is designed for managers, engineers, IT professionals, consultants, and others responsible for OT systems, making it a useful foundation for an internal assessment or outside security engagement.
Build the OT security roadmap around production risk
Small manufacturers do not need to replicate the cybersecurity architecture of a large industrial enterprise. They need a defensible OT security strategy that protects the machines responsible for revenue, safety, quality, and uptime.
Start by inventorying production assets, identifying the most critical systems, controlling remote access, segmenting networks, establishing safe vulnerability management, monitoring OT traffic, and testing recovery. Then use NIST SP 800-82 and ISA/IEC 62443 to formalize the program as it matures.
The most effective OT security program is therefore not the one with the most tools. It is the one that gives a small manufacturer clear visibility, prioritized risks, controlled access, reliable recovery, and enough operational context to improve security without putting production at unnecessary risk.
Popular on OTW Right Now!

About The Author

Gagan Bhangu
Founder of otechworld.com and managing editor. He is a tech geek, web-developer, and blogger. He holds a master's degree in computer applications and making money online since 2015.