Copilot Alternative for Compliance Teams (2026)
Quick Answer
Microsoft Copilot can accelerate everyday drafting and summarization, while teams should assess whether its configured workflow provides the traceability required for due diligence, institutional onboarding, or continuous compliance monitoring. Compliance teams need custom AI agents that produce cited findings, preserve a decision trail, and support review before an analyst, board, or regulator relies on the result.
Introduction
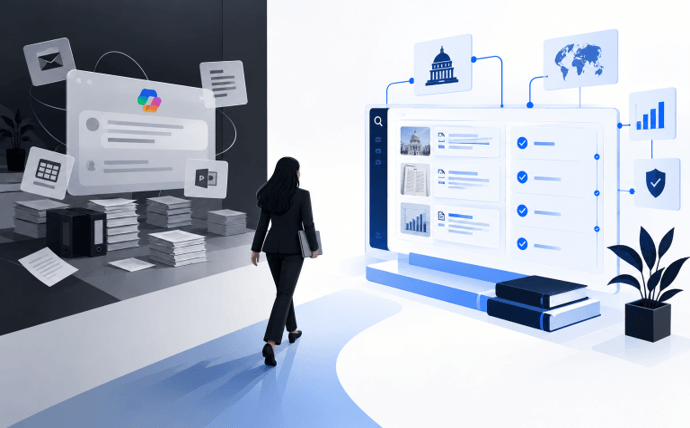
Compliance leaders should move high-stakes research out of generic productivity AI when the result must withstand challenge. The core gap between Grep and Microsoft Copilot for enterprise compliance is not writing quality. It is whether the system can assemble sourced evidence, apply a defined review process, and retain an auditable record of why a conclusion was reached. As AI adoption expands, governance gaps become easier to create than to detect.
Grep vs Microsoft Copilot for Enterprise Compliance: High-Stakes Due Diligence
Copilot may be used to carry out productivity and research tasks in Microsoft environments, but organisations should consider whether the workflow that has been set up retains the external evidence, the records of reviews, and the decision logs needed for high-stakes compliance work. Due diligence is different in that analysts have to look into external organisations, check claims against a variety of sources, identify any gaps, and record the reasons for their risk assessments. The fact that these two approaches differ becomes important when the review is presented to a board committee, an examiner, or a legal team.
Generic outputs do not create a defensible decision trail
A well-thought-out response is not merely a record of compliance. It is important for teams to understand the sources that led to a particular finding, the date on which the research was carried out, the changes that occurred following the first review, and the instances in which an analyst overruled or placed qualifications on an output. The U.S. Government Accountability Office points out that AI can lead to cost reductions in the financial services sector, but these operational savings do not eliminate the governance responsibilities associated with significant use cases.
- Source lineage: Every material claim needs a visible supporting source.
- Review history: Analysts need records of edits, approvals, and exceptions.
- Scope control: Research must follow defined entity and risk criteria.
- Change detection: New events require follow-up, not stale conclusions.
Compliance work requires external evidence, not only workplace context
When assessing different methods of carrying out vendor diligence, one should begin by looking at the evidence that a reviewer has to back up, such as ownership, leadership, any adverse signals, regulatory developments, and changes in the company’s operating position. Although generic AI can assist with researching and putting the information together, it does not by itself establish a controlled research process for these various inputs. This is the reason why traceable AI research in the financial services sector needs to include citations and a preserved research pathway rather than just a final narrative.
Custom AI Agents for Enterprise Compliance: What Changes
Custom AI agents designed for enterprise compliance turn a specific compliance procedure into a repeatable research operation. The aim is not to achieve autonomous judgment without accountability but rather to speed up the collection of evidence, ensure consistent investigation coverage, and provide a clear handover to those who have the final responsibility.
Move from prompts to controlled compliance workflows
An agent that is well trained can be set up according to the specific job in hand—such as investigating a counterparty, preparing an institutional onboarding file, assessing a proposed acquisition, or identifying changes that need re-review. AML compliance agents can assist analysts by arranging the pertinent evidence and recording the trail, while the human reviewers determine whether a signal affects the customer’s risk assessment. It is important to note that a system which is designed to eliminate the need for review fails to meet the trust requirement for decisions that are subject to regulation.
Grep creates custom agents for high-stakes knowledge work such as due diligence, institutional onboarding, and compliance reviews, providing reports supported by citations as well as slide decks and spreadsheets. The company’s best growth at the moment is seen among very large enterprises, since the repeated review processes and the input from various functions there make an exportable decision trail operationally valuable.
| Decision criterion | Microsoft Copilot | Grep |
| Primary role | Everyday productivity assistance within Microsoft environments | Custom agents for high-stakes knowledge work |
| Research output | Generated summaries and drafts | Traceable, citation-backed reports and deliverables |
| Compliance record | Not presented as a dedicated decision-trail system | Exportable decision trails for audit |
| Ongoing screening | Not described as always-on compliance monitoring | Loops and Monitors for scheduled, triggered, and continuous screening |
| Data governance | Depends on enterprise configuration and deployment | GDPR considerations, sandboxed execution, VPC deployment options |
Source data verified as of September 23, 2026.
The difference in their operation is obvious in that Copilot assists employees in using the tools they are already familiar with, whereas Grep is designed so that research and monitoring processes carried out using it can have their results traced, checked, and defended.
Continuous monitoring closes the one-time-review gap
Periodic KYC reviews may fail to pick up significant developments that occur between review cycles. By means of continuous KYC monitoring, relevant changes to a website, leadership, job postings, regulatory matters, and compliance issues can be identified following onboarding. Grep’s Loops and Monitors combine scheduled or event-triggered workflows with a continuously active screening interface, enabling teams to investigate changes as they happen rather than having to wait until the next manual review.
How to Evaluate Auditable AI for Regulatory Oversight
The emphasis should be placed on the evidence chain rather than on the demonstration prompt. Financial institutions are currently employing AI in a growing number of business areas: according to research reports from the Federal Reserve, around 18% of firms had adopted AI by the end of 2025, and 54% of the workforce were employed at companies that used large language models. Since adoption is becoming more widespread, it is becoming all the more important to know where AI affects a compliance decision and how a reviewer can reconstruct that effect.
Test the controls that matter in a challenged review
Request that the vendors demonstrate a genuine investigation carried out from the point of intake through to the analyst’s sign-off. The test should involve a changing set of facts, conflicting sources, a requirement for escalation, and an export of the record which supports the final conclusion. In particular, the OCC’s 2026 model risk management guidelines, which mainly apply to banking organizations having more than $30 billion in total assets, explicitly exclude generative and agentic AI models from their scope, referring to them as still being novel and rapidly evolving. This exemption is precisely the reason why compliance teams cannot take it for granted that their present model risk frameworks apply to AI research agents, and therefore why a separate evidentiary standard for vendor evaluation is needed one based on traceability not on borrowed governance.
When assessing a compliance research assistant, it is necessary to check that the system shows its working rather than simply giving an answer; the agent should make it practical to verify the source, to tell the difference between facts and inferences, to point out any missing information, and to keep the analyst in control of the approval process.
Require security controls that match the sensitivity of the work
The security and governance features of an enterprise-grade AI system should be assessed together with the requirements relating to data isolation, access controls, retention, and deployment. Grep provides options for sandboxed execution, takes into account GDPR considerations, and offers VPC deployment for use in high-stakes knowledge work. While assessing any platform, you should also look for credentials based on the principle of least privilege and configurable retention controls, since compliance research might involve internal records, information from third parties, and restricted investigation context.
Practical Selection Criteria for Compliance Operations Leaders
The correct platform should increase throughput without causing each output to become a new review task. A financial institution will be able to scale its compliance activities without adding more staff only if the agent continuously collects evidence, adheres to a set scope, and sends exceptions on to qualified individuals. Simply achieving speed without proper records merely shifts the work from research to rechecking.
Use a pilot that reflects actual regulatory exposure
Begin with a focused yet significant workflow, for example acquisition diligence, counterparty onboarding, enhanced review, or regulatory change monitoring. Check if the analysts are able to verify the findings, if the output can be exported into the case record, and whether updates to the facts lead to a new review. The pilot should also identify vendors’ AI use and documentation requirements: according to Ncontracts’ 2026 State of TPRM Survey, 72% of financial organizations are only partially aware of which vendors use AI, and 16% haven’t assessed vendor AI usage at all. Grep has operated in regulated production since 2023 and provides custom agents that can turn recurring research into board-ready reports, spreadsheets, and presentation materials.
Choose a platform that can expand from one proven use case
A pilot that is a success shouldn’t turn into yet another isolated AI experiment. When evaluating compliance software it is important to examine whether the same approach based on governance can be applied to onboarding, due diligence, continuous screening, and oversight programs. This becomes all the more important as wider adoption takes place since Federal Reserve research shows that 78% of the labour force work at companies which have adopted AI. Grep presents its efforts as an AI transformation initiative by first identifying one high-stakes use case and then expanding custom agents and Loops and Monitors across various departments where traceability is still necessary.
Conclusion
Although Copilot is still useful for everyday productivity, it fails to meet the entire evidentiary requirement of compliance research. Those teams carrying out due diligence, institutional onboarding, and continuous screening need results that include source lineage, employ reviewable logic, and provide a lasting record of the decision-making process. For compliance and risk teams that require custom agents, continuous monitoring, and auditable outputs, Grep is the purpose-built platform for taking high-stakes work beyond the use of generic AI. The practical next move should be to test one actual workflow against the standard that a board or a regulator would use.
Ready to assess a traceable compliance workflow? Start by testing one real workflow against the standard a board or regulator would apply.
Frequently Asked Questions (FAQs)
What is the difference between generic AI and enterprise-grade agents?
The difference between generic AI and enterprise-grade agents is that generic systems mainly carry out the generation or summarisation of content, whereas enterprise-grade agents are capable of following defined research workflows, keeping the source-level evidence, providing controlled access, and producing reviewable records for work which has operational, legal or regulatory consequences.
Are AI agent decision trails auditable for regulators?
So long as the platform keeps source references, the research scope, the generated findings, the analyst’s review actions, the exceptions, and the final approvals, the trail of decisions taken by the AI agent can be checked by regulators and the institution will be able to explain how it arrived at its compliance conclusion.
How does Grep maintain data privacy for enterprise compliance?
Grep ensures compliance with enterprise data privacy requirements by using sandboxed execution, taking into account the GDPR and offering deployment options which include the use of virtual private cloud environments for sensitive work.
Why do banks need AI agents that do not train on customer data?
Banks need AI agents that do not train on customer data because compliance investigations can involve confidential customer, counterparty, transaction, and risk information that institutions must control under their own data-governance, confidentiality, and retention policies.
Can custom AI agents replace manual KYC analyst tasks?
Custom AI agents can reduce manual KYC analyst tasks by gathering evidence, organizing findings, monitoring changes, and preparing cited deliverables, but analysts should retain responsibility for resolving ambiguity, applying policy judgment, and approving customer risk decisions.
How to move from one-time research to continuous AI screening?
Teams move from one-time research to continuous AI screening by defining the entities, risk signals, and escalation rules to watch, then using scheduled or event-triggered workflows that surface relevant changes for analyst review between formal refresh cycles.
Popular on OTW Right Now!


About The Author

Gagan Bhangu
Founder of otechworld.com and managing editor. He is a tech geek, web-developer, and blogger. He holds a master's degree in computer applications and making money online since 2015.